Security policies
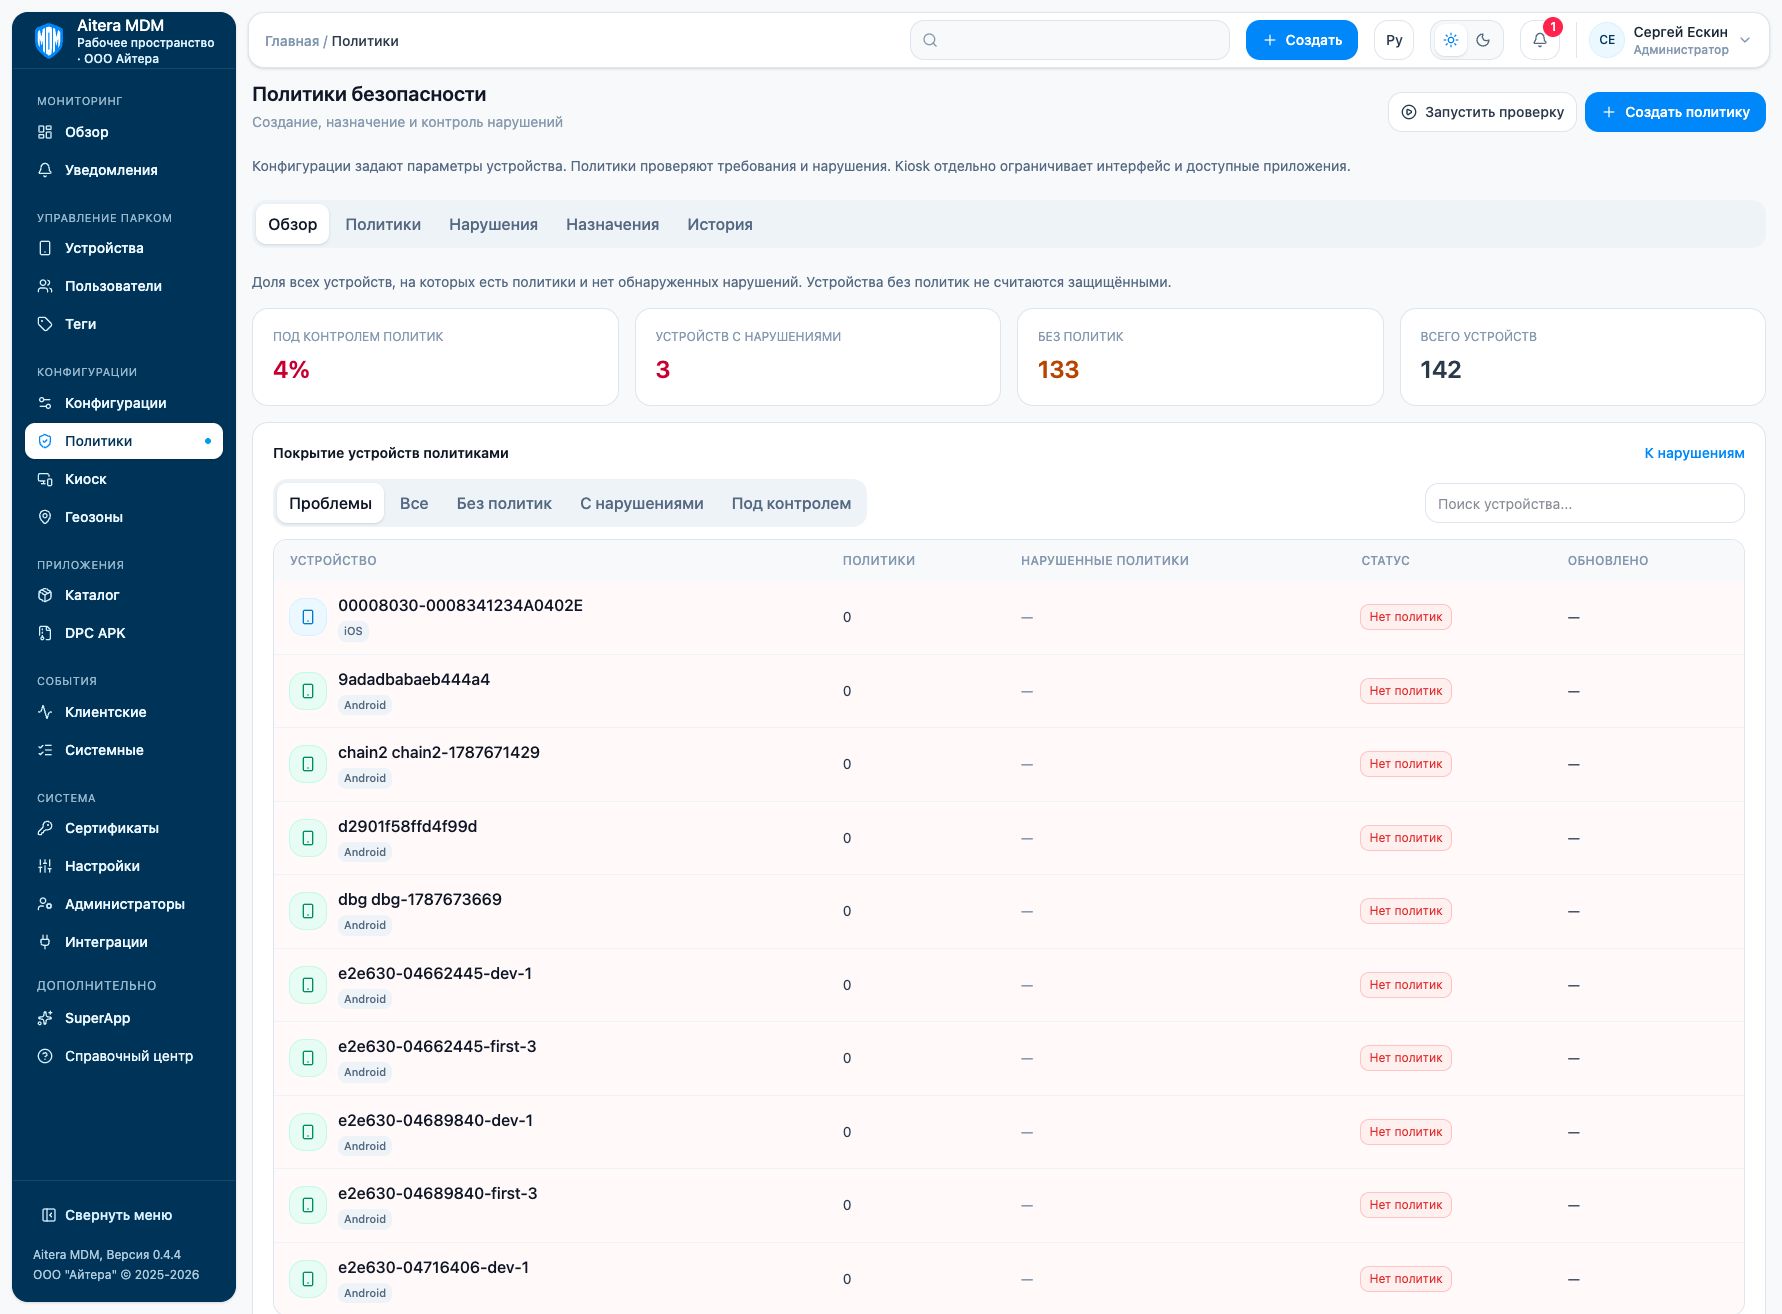
A policy defines a security requirement and the response to a violation. The assignment determines the devices to which the requirement applies.
Four types are available in the console: compromised device, data protection disabled, MDM disabled, and prolonged loss of contact. Each type has its own signals and parameters. The check depends on the telemetry received: the absence of fresh data does not confirm compliance. Before assigning, verify the management channel, the device mode, and the availability of the required signal.
Parameters visible in the form are not always included in the save request. For the current interface this is noted separately in the type references. The response runs after a violation is detected and depends on the management channel, connectivity, and the device’s support for the command; an entry in the history does not by itself confirm execution. Locking in the native DPC is a screen lock, not Lost Mode or setting a device PIN.
References and instructions
- Creating and assigning a policy
- Compliance control
- Compromised device
- Data protection disabled
- MDM disabled
- Prolonged loss of contact
- Responses to a violation
For the current state of a device, take into account client events and telemetry. For Android, first determine the management channel, DPC or Android Enterprise.